Tổng hợp các tools hỗ trợ phân tích mã độc (malware analysis)

Trong post này tôi sẽ cập nhật những tools thú vị và bổ ích dùng để hỗ trợ quá trình phân tích và xử lý mã độc:
1. oletools:
Python tools to analyze MS OLE2 files (Structured Storage, Compound File Binary Format) and MS Office documents, for malware analysis, forensics and debugging. http://www.decalage.info/python/oletools
2. AVCLASS++: Massive Malware Labeling Tool
AVCLASS++ is a labeling tool for creating a malware dataset. Addressing malware threats requires constant efforts to create and maintain a dataset. Especially, labeling malware samples is a vital part of shepherding a dataset. AVCLASS, a tool developed for this purpose, takes as input VirusTotal reports and returns labels that aggregates scan results of multiple anti-viruses. And now, AVCLASS++ is shipped with the brand-new capacities!
In a nutshell, AVCLASS++ enables the following operation:
- Input:
- VirusTotal report(s)
- Malware binar(y|ies) (optional)
- Output:
- Malware label(s) (family name)
3. Multiscanner - Modular File Scanning/Analysis Framework
MultiScanner is a file analysis framework that assists the user in evaluating a set of files by automatically running a suite of tools for the user and aggregating the output.
Input: Malware samples --> Processing: MultiScanner (analysyt metadata + Automated Analysis Tools + Manual Analysis Tools + Data Analytics) --> Output: Reports

4. SysAnalyzer: Automated malcode analysis system
The main components of SysAnalyzer work off of comparing snapshots of the system over a user-specified time interval. By using a snapshot system, we can effectively present viewers with only the persistent changes found on the system since the application was first to run.
Note: SysAnalyzer is not a sandboxing utility. Target executables are run in a fully live test on the system. If you are testing malicious code, you must realize you will be infecting your test system.
SysAnalyzer’s is designed to take snapshots of the following system attributes:
* Running processes
* Open ports and associated process
* DLLs loaded into explorer.exe and Internet Explorer
* System Drivers loaded into the kernel
* Snapshots of certain registry keys
5. SSMA - Simple Static Malware Analyzer
Features:
- Searches for websites, e-mail addresses, IP addresses in the strings of the file.
- Looks for Windows functions commonly used by malware.
- Get results from VirusTotal and/or upload files.
- Malware detection based on Yara-rules - https://virustotal.github.io/yara/
- Detect well-known software packers.
- Detect the existence of cryptographic algorithms.
- Detect anti-debug and anti-virtualization techniques used by malware to evade automated analysis.
- Find if documents have been crafted to leverage malicious code.

Usage:
git clone https://github.com/secrary/SSMA
cd SSMA
sudo pip3 install -r requirements.txt
python3 ssma.py -h
5. DrSemu - Malware Detection And Classification Tool Based On Dynamic Behavior

DrSemu runs executables in an isolated environment, monitors the behavior
of a process, and based onDr.Semurules created by you or the community,
detects if the process is malicious or not.
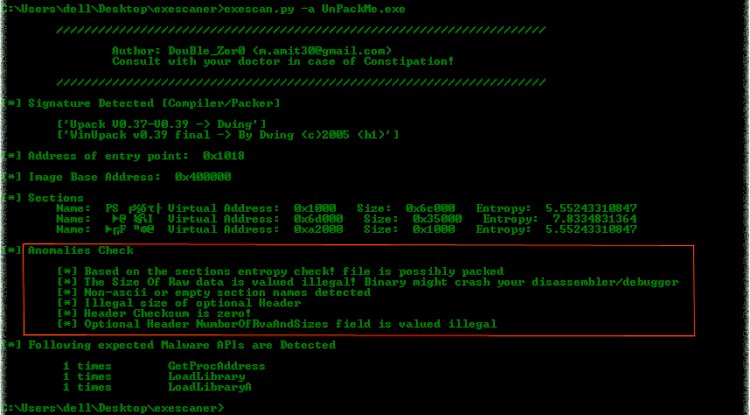
6. ExeScan - FREE console based tool to detect anomalies in PE
ExeScan is the FREE console based tool to detect anomalies in PE (Portable Executable) files. It quickly scans given executable file and detect all kind of anomalies in its PE header fields including checksum verifications, size of various header fields, improper size of raw data, non-ascii/empty section names etc. Various packers/protectors mod…
7. Bộ công cụ của Kahusecurity
Link
CÁC BÀI VIẾT, BLOG LIÊN QUAN
1. Basic Malware Analysis Tools
Link
2. Dynamic Malware Analysis Tools
Link
3. Most Important Security Tools and Resources For Security Researcher and Malware Analyst
Link
4. Practical Malware Analysis Starter Kit
Link
5. https://github.com/albertzsigovits/mal-analysis-tools
Static string analysis:
Linux:
file
trid
strings
floss
exiftool
imphash
ssdeep
authentihash
bulk-extractor
uudeview
foremost
scalpel
steghide
stegsnow
zsteg
PEpper - https://github.com/Th3Hurrican3/PEpper
pev
pecarve
pescanner.py
analysePE.py
AnalyzePE
upx
yara
ripPE - https://github.com/matonis/ripPE
Unipacker - https://github.com/unipacker/unipacker
Windows:
CFF Explorer - https://ntcore.com/?page_id=388
Resource Hacker - http://www.angusj.com/resourcehacker
XN Resource Hacker - https://stefansundin.github.io/xn_resource_editor
Dependency Walker - http://www.dependencywalker.com
LordPE - http://www.woodmann.com/collaborative/tools/images/Bin_LordPE_2010-6-29_3.9_LordPE_1.41_Deluxe_b.zip
Scylla - https://github.com/NtQuery/Scylla
Detect It Easy - https://ntinfo.biz
PE Explorer - http://www.heaventools.com/overview.htm
Import REConstructor - https://github.com/NtQuery/Scylla
LordPE - https://www.aldeid.com/wiki/LordPE
PEiD - https://www.aldeid.com/wiki/PEiD
PEview - https://www.aldeid.com/wiki/PEView
FileAlyzer - https://www.safer-networking.org/products/filealyzer/
PEstudio - https://www.winitor.com/
Chimprec - https://www.aldeid.com/wiki/CHimpREC
PE Insider - https://cerbero.io/peinsider/
PEframe - https://github.com/guelfoweb/peframe
UPX - https://github.com/upx
Manalyze - https://github.com/JusticeRage/Manalyze
PortEx - https://github.com/katjahahn/PortEx
Signsrch - https://aluigi.altervista.org/mytoolz/signsrch.zip
Revelo - http://www.kahusecurity.com/2012/05/revelo-javascript-deobfuscator
UniExtract2 - https://github.com/Bioruebe/UniExtract2
MalUnpack - https://github.com/hasherezade/mal_unpack
PE_recovery_tools - https://github.com/hasherezade/pe_recovery_tools
Auto XOR decrypter - https://github.com/MRGEffitas/scripts/blob/master/auto_xor_decryptor.py
Live dynamic detonation:
Proxy
Fiddler - https://www.telerik.com/fiddler
Burp Suite - https://portswigger.net/burp/communitydownload
MitM
FakeDNS - https://www.fireeye.com/services/freeware/apatedns.html
ApateDNS - https://github.com/Crypt0s/FakeDns
C2
FakeNet - https://github.com/fireeye/flare-fakenet-ng
INetSim - https://www.inetsim.org
netcat - http://netcat.sourceforge.net
TCPView - https://docs.microsoft.com/en-us/sysinternals/downloads/tcpview
Wireshark - https://www.wireshark.org
Imaginary C2 - https://github.com/felixweyne/imaginaryC2
Suricata - https://suricata-ids.org/download/
Emerging Threat SIGs - https://rules.emergingthreats.net/
Tor - https://www.torproject.org/
Registry
RegShot - https://sourceforge.net/projects/regshot
WhatChanged - https://www.majorgeeks.com/files/details/what_changed.html
CaptureBAT - https://www.honeynet.org/node/315
Process
Process Hacker - https://github.com/processhacker/processhacker
Process Monitor - https://docs.microsoft.com/en-us/sysinternals/downloads/procmon
Process Explorer - https://docs.microsoft.com/en-us/sysinternals/downloads/process-explorer
ProcessSpawnControl - https://github.com/felixweyne/ProcessSpawnControl
ProcDOT - http://www.procdot.com
API
API Monitor - http://www.rohitab.com/apimonitor#Download
APISpy - http://www.matcode.com/apis32.htm
Persistance
Autoruns - https://docs.microsoft.com/en-us/sysinternals/downloads/autoruns
Memory
volatility - https://github.com/volatilityfoundation/volatility
Memoryze - https://www.fireeye.com/services/freeware/memoryze.html
OSR Driver Loader - https://www.aldeid.com/wiki/OSR-Driver-Loader
The Sleuth Kit - https://github.com/sleuthkit/sleuthkit
Truman - http://nsmwiki.org/Truman_Overview
yara - https://github.com/virustotal/yara
Frameworks
mastiff - https://github.com/KoreLogicSecurity/mastiff
IRMA - https://github.com/quarkslab/irma
VIPER - https://github.com/viper-framework/viper
Loki - https://github.com/Neo23x0/Loki
Multiscanner - https://github.com/mitre/multiscanner
chopshop - https://github.com/MITRECND/chopshop
Munin - https://github.com/Neo23x0/munin
Fenrir - https://github.com/Neo23x0/Fenrir
Harpoon - https://github.com/Neo23x0/harpoon
Manual reverse engineering:
PE:
Online - https://onlinedisassembler.com/static/home/index.html
IDA - https://www.hex-rays.com/products/ida/
Hex-Rays Decompiler - https://www.hex-rays.com/products/decompiler/
radare2 - https://github.com/radare/radare2
Binary Ninja - https://binary.ninja/
BinDiff - https://www.zynamics.com/bindiff.html
BinNavi - https://github.com/google/binnavi
Bochs - http://bochs.sourceforge.net/getcurrent.html
x64dbg - https://x64dbg.com/#start
WinDbg - https://docs.microsoft.com/en-us/windows-hardware/drivers/debugger/debugger-download-tools
OllyDbg - http://www.ollydbg.de/
ImmunityDbg - https://www.immunityinc.com/products/debugger/
Shellcode:
xorsearch - https://blog.didierstevens.com/2014/09/29/update-xorsearch-with-shellcode-detector/
scdbg - http://sandsprite.com/blogs/index.php?uid=7&pid=152
shellcode2exe - https://zeltser.com/convert-shellcode-to-assembly/
jmp2it - https://digital-forensics.sans.org/blog/2014/12/30/taking-control-of-the-instruction-pointer/
BlobRunner - https://github.com/OALabs/BlobRunner
.NET:
dnSpy - https://github.com/0xd4d/dnSpy
dotPeek - https://www.jetbrains.com/decompiler
ILSpy - https://github.com/icsharpcode/ILSpy
JustDecompile - https://www.telerik.com/products/decompiler.aspx
JustAssembly - https://www.telerik.com/justassembly
Reflector - https://www.red-gate.com/products/dotnet-development/reflector/index
CodeReflect - http://www.devextras.com/decompiler
Dis# - http://www.netdecompiler.com
IL Disassembler - https://www.dotnetperls.com/il-disassembler
Disassembly Diagnoser - https://adamsitnik.com/Disassembly-Diagnoser
JS:
V8 - https://isc.sans.edu/diary/V8+as+an+Alternative+to+SpiderMonkey+for+JavaScript+Deobfuscation/12157
box-js - https://github.com/CapacitorSet/box-js
js-detox - https://github.com/svent/jsdetox
Flash:
SWFDec - https://cgit.freedesktop.org/wiki/swfdec
swf_mastah.py - https://github.com/9b/pdfxray_lite/blob/master/swf_mastah.py
VBA:
ViperMonkey - https://github.com/decalage2/ViperMonkey
olevba.py - https://github.com/decalage2/oletools/wiki/olevba
OLE:
OfficeMalScanner - http://www.reconstructer.org/code/OfficeMalScanner.zip
OLETools - https://www.decalage.info/python/oletools
Hachoir - https://bitbucket.org/haypo/hachoir/wiki/hachoir-urwid
EXEFilter - http://www.decalage.info/exefilter
RTF:
rtfproc
rtfprocrule
rtfraptor
rtfscan
rtfobj
rtfparser
rtfdump
PDF:
PDF Stream Dumper - http://sandsprite.com/blogs/index.php?uid=7&pid=57
PDF Dissector - https://blog.zynamics.com/2010/09/03/pdf-dissector-1-7-0-released/
PDF Tools - https://blog.didierstevens.com/programs/pdf-tools/
pdfid.py - https://blog.didierstevens.com/programs/pdf-tools/
pdfparser.py - https://blog.didierstevens.com/programs/pdf-tools/
peepdf.py - https://github.com/jesparza/peepdf
qpdf - http://qpdf.sourceforge.net/
pdfinfo
pdf2txt
pdfdetach
Other:
Kahusecurity Tools - http://www.kahusecurity.com/tools.html
DidierStevensSuite - https://github.com/DidierStevens/DidierStevensSuite
Awesome Malware Analysis list - https://github.com/rshipp/awesome-malware-analysis
Awesome Reversing list - https://github.com/tylerha97/awesome-reversing
Remnux - https://remnux.org/
SANS SIFT - https://digital-forensics.sans.org/community/downloads
FireEye FLARE-VM - https://github.com/fireeye/flare-vm
FireEye CommandoVM - https://github.com/fireeye/commando-vm
Webshell-intel - https://github.com/Neo23x0/webshell-intel
Malware-behaviors - https://github.com/MAECProject/malware-behaviors
MalTrail - https://github.com/stamparm/maltrail
YARA:
YaraScanner - https://github.com/mitre/yararules-python
Yara Analyzer - https://github.com/Neo23x0/yarAnalyzer
Yara Generator - https://github.com/Neo23x0/yarGen
Awesome-Yara - https://github.com/Neo23x0/awesome-yara
Malware-signatures - https://github.com/Neo23x0/malware-signatures
Signature-set - https://github.com/Neo23x0/signature-base
Yara-rules - https://github.com/Neo23x0/rules
mkYARA - https://blog.fox-it.com/2019/03/28/mkyara-writing-yara-rules-for-the-lazy-analyst/
VirusTotal:
VT Investigator paper - https://storage.googleapis.com/vt-gtm-wp-media/virustotal-for-investigators.pdf
Detection and Classification
Antivirus and other malware identification tools
- AnalyzePE - Wrapper for a variety of tools for reporting on Windows PE files.
- Assemblyline - A scalable distributed file analysis framework.
- BinaryAlert - An open source, serverless AWS pipeline that scans and alerts on uploaded files based on a set of YARA rules.
- chkrootkit - Local Linux rootkit detection.
- ClamAV - Open source antivirus engine.
- Detect It Easy(DiE) - A program for determining types of files.
- Exeinfo PE - Packer, compressor detector, unpack info, internal exe tools.
- ExifTool - Read, write and edit file metadata.
- File Scanning Framework - Modular, recursive file scanning solution.
- Generic File Parser - A Single Library Parser to extract meta information,static analysis and detect macros within the files.
- hashdeep - Compute digest hashes with a variety of algorithms.
- HashCheck - Windows shell extension to compute hashes with a variety of algorithms.
- Loki - Host based scanner for IOCs.
- Malfunction - Catalog and compare malware at a function level.
- Manalyze - Static analyzer for PE executables.
- MASTIFF - Static analysis framework.
- MultiScanner - Modular file scanning/analysis framework
- Nauz File Detector(NFD) - Linker/Compiler/Tool detector for Windows, Linux and MacOS.
- nsrllookup - A tool for looking up hashes in NIST's National Software Reference Library database.
- packerid - A cross-platform Python alternative to PEiD.
- PE-bear - Reversing tool for PE files.
- PEframe - PEframe is an open source tool to perform static analysis on Portable Executable malware and malicious MS Office documents.
- PEV - A multiplatform toolkit to work with PE files, providing feature-rich tools for proper analysis of suspicious binaries.
- PortEx - Java library to analyse PE files with a special focus on malware analysis and PE malformation robustness.
- Quark-Engine - An Obfuscation-Neglect Android Malware Scoring System
- Rootkit Hunter - Detect Linux rootkits.
- ssdeep - Compute fuzzy hashes.
- totalhash.py - Python script for easy searching of the TotalHash.cymru.com database.
- TrID - File identifier.
- YARA - Pattern matching tool for analysts.
- Yara rules generator - Generate yara rules based on a set of malware samples. Also contains a good strings DB to avoid false positives.
- Yara Finder - A simple tool to yara match the file against various yara rules to find the indicators of suspicion.
6. Sysinternal Suite
Download windows Sysinternals suite and explore the listed tools for malware hunting and securing your windows system.
|
Tools |
Description |
|
AccessEnum |
This tool shows access permission of user accounts to the directories, files and Registry keys on the system. Users can use it to find ACL permission holes |
|
EFSDump |
View information for encrypted files |
|
MoveFile |
Schedule file rename and delete commands for the next reboot. This can be useful for cleaning stubborn or in-use malware files |
|
PendMoves |
See what files are scheduled for delete or rename the next time the system boots |
|
Process Monitor |
Monitor file system, Registry, process, thread and DLL activity in real-time |
|
Psfile |
See what files are opened remotely |
|
Sdelete |
Securely overwrite your sensitive files and cleanse your free space of previously deleted files using this DoD-compliant secure delete program |
|
ShareEnum |
Scan file shares on your network and view their security settings to close security holes |
|
Sigcheck |
Dump file version information and verify that images on your system are digitally signed |
|
Ping |
Measures network performance |
|
TCPview |
Active socket command-line viewer |
|
Whois |
See who owns an Internet address |
|
Autoruns |
See what programs are configured to startup automatically when your system boots and you login. Autoruns also shows you the full list of Registry and file locations where applications can configure auto-start settings. |
|
Handle |
This handy command-line utility will show you what files are open by which processes, and much more |
|
ListDLLs |
List all the DLLs that are currently loaded, including where they are loaded and their version numbers. Version 2.0 prints the full path names of loaded |
|
ProcDump |
This new command-line utility is aimed at capturing process dumps of otherwise difficult to isolate and reproduce CPU spikes. It also serves as a general process dump creation utility and can also monitor and generate process dumps when a process has a hung window or unhandled exception |
|
Process Explorer |
Find out what files, registry keys, and other objects processes have open, which DLLs they have loaded, and more. This uniquely powerful utility will even show you who owns each process. |
|
Psexec |
Execute processes remotely |
|
Pskill |
Terminate local or remote processes |
|
Pslist |
Show information about processes and threads |
|
Psservice |
View and control services |
|
Pssuspend |
Suspend and resume processes |
|
Shellrunas |
Launch programs as a different user via a convenient shell context-menu entry |
|
Autologon |
Bypass password screen during logon |
|
LogonSessions |
List active logon sessions |
|
PsLoggedOn |
Show users logged on to a system |
|
Psinfo |
Obtain information about a system |
|
Strings |
Search for ANSI and UNICODE strings in binary images. |
7.
What's Your Reaction?